Products Open beta
AZET Shield
Brute-force and bot protection for the servers you run. An agent on your Linux server bans attacking addresses at the firewall, and a hosted dashboard shows what was blocked and mails you when it happens.
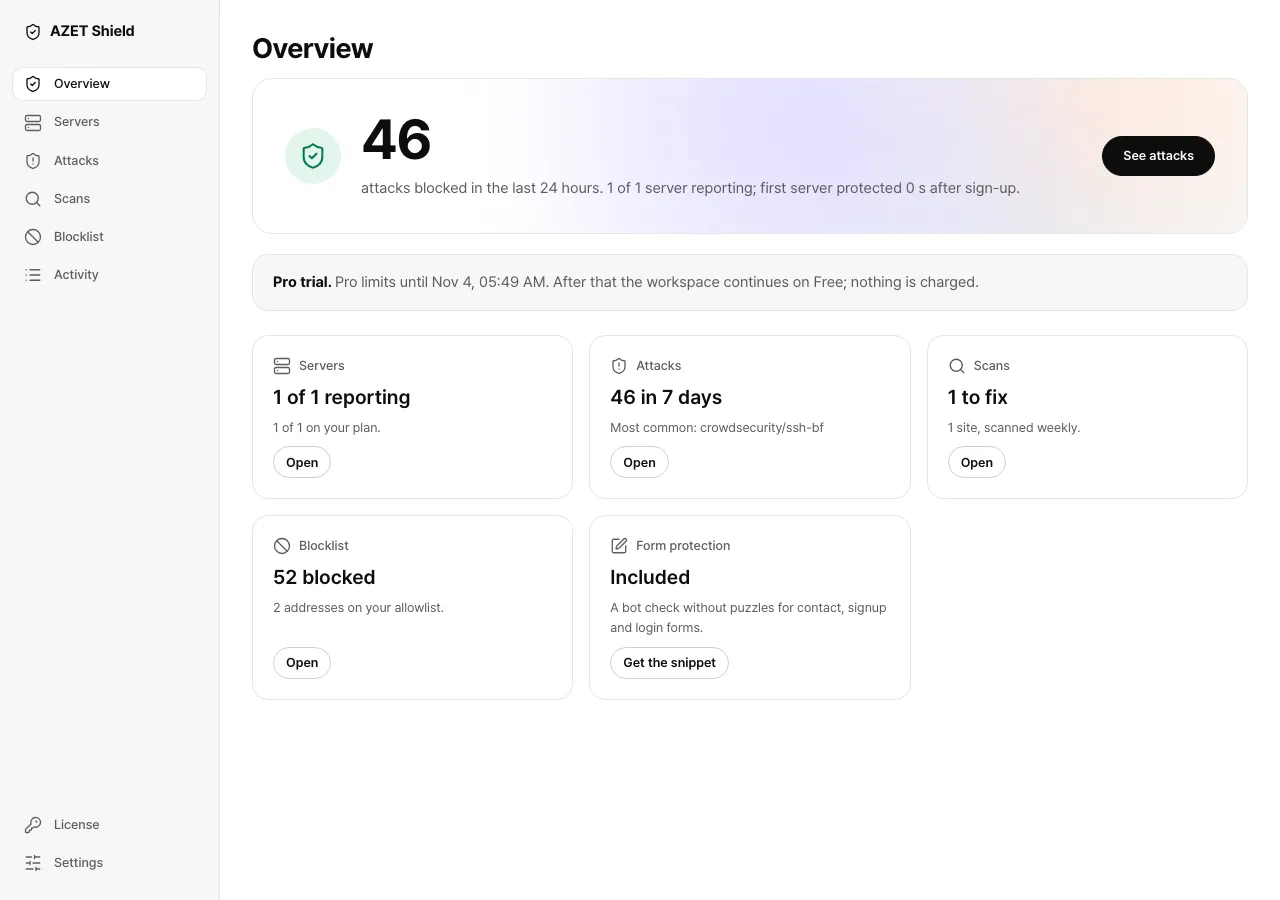
What works today
Server agent
One command installs it on a Debian or Ubuntu server, or on the RHEL family (RHEL, Rocky Linux, AlmaLinux, CentOS Stream, Fedora, Amazon Linux 2023). When an address trips a rule, such as repeated failed SSH logins, the server bans it at the firewall.
Blocklists
Each server also receives addresses that attacked your other servers, addresses you add by hand, and a community list of addresses reported by at least three separate workspaces in the last seven days. Each list can be switched off.
Allowlist
The address you install from is allowlisted before blocking starts, so you do not lock yourself out. An allowlisted address is never banned, and you can add more from the dashboard.
Email alerts
When attacks are blocked, the dashboard mails the address you confirmed, at most once per server per hour, with an unsubscribe link in every mail. You also get one mail when a server stops reporting (with the time of its last report and the command to check it) and a daily summary at 09:00 KST on days your servers blocked attacks.
Vulnerability scans
Scheduled scans run on our hosted scanner, only against sites you have proved you own: once a month on Free, weekly on Pro and daily on Business. Ownership is checked again before each scan.
Dashboard
Overview, Servers, Attacks, Blocklist and Activity at shield.azet.io. There are no accounts: creating a workspace shows an access token once, and that token is how you sign in, so keep it somewhere safe. If it is lost, the sign-in page mails a sign-in link to the address you confirmed.
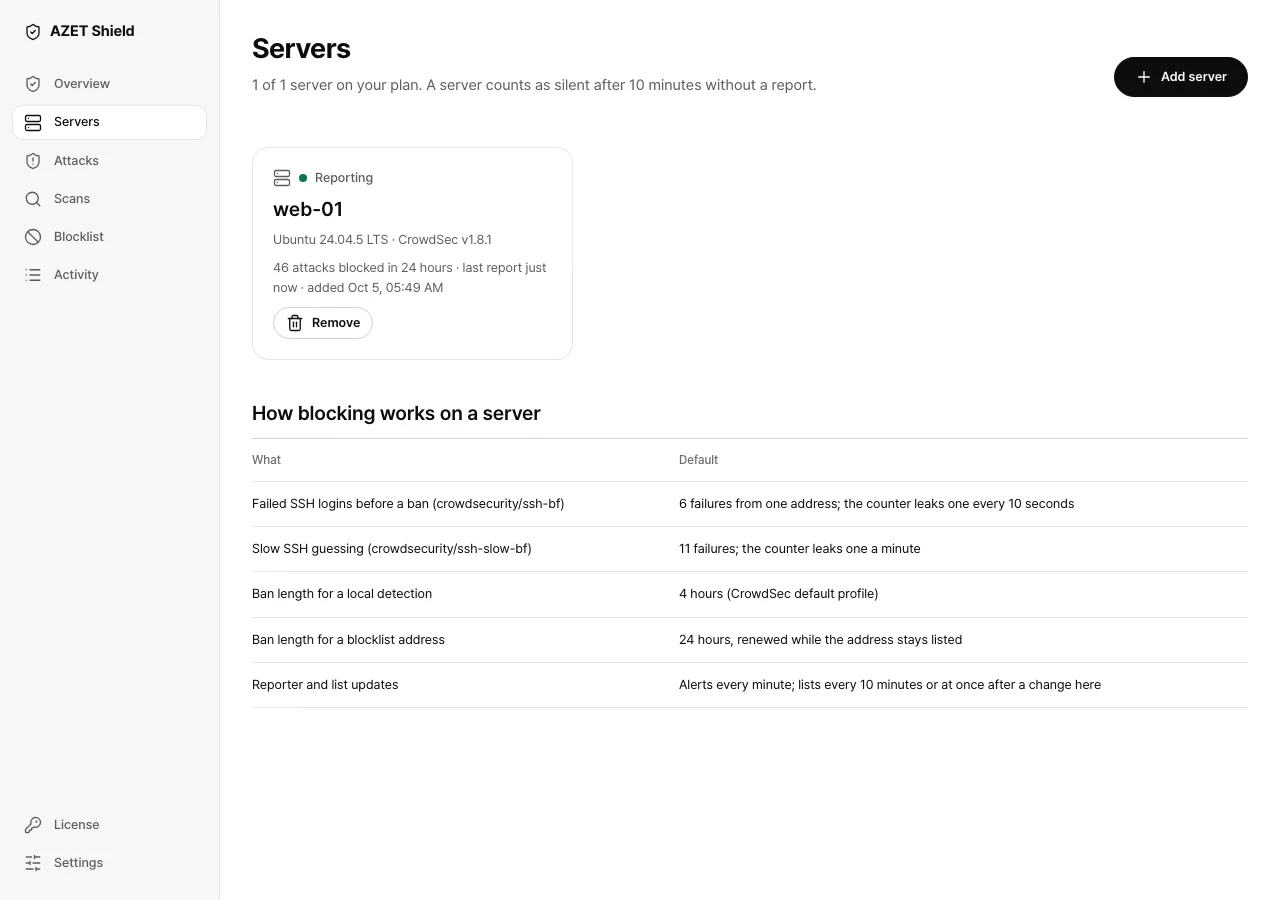
Servers
Server agent. It installs the unmodified open-source CrowdSec engine and its firewall component from CrowdSec’s own package repository, with detection rules for SSH, nginx and WordPress. An uninstall script removes what the installer added.
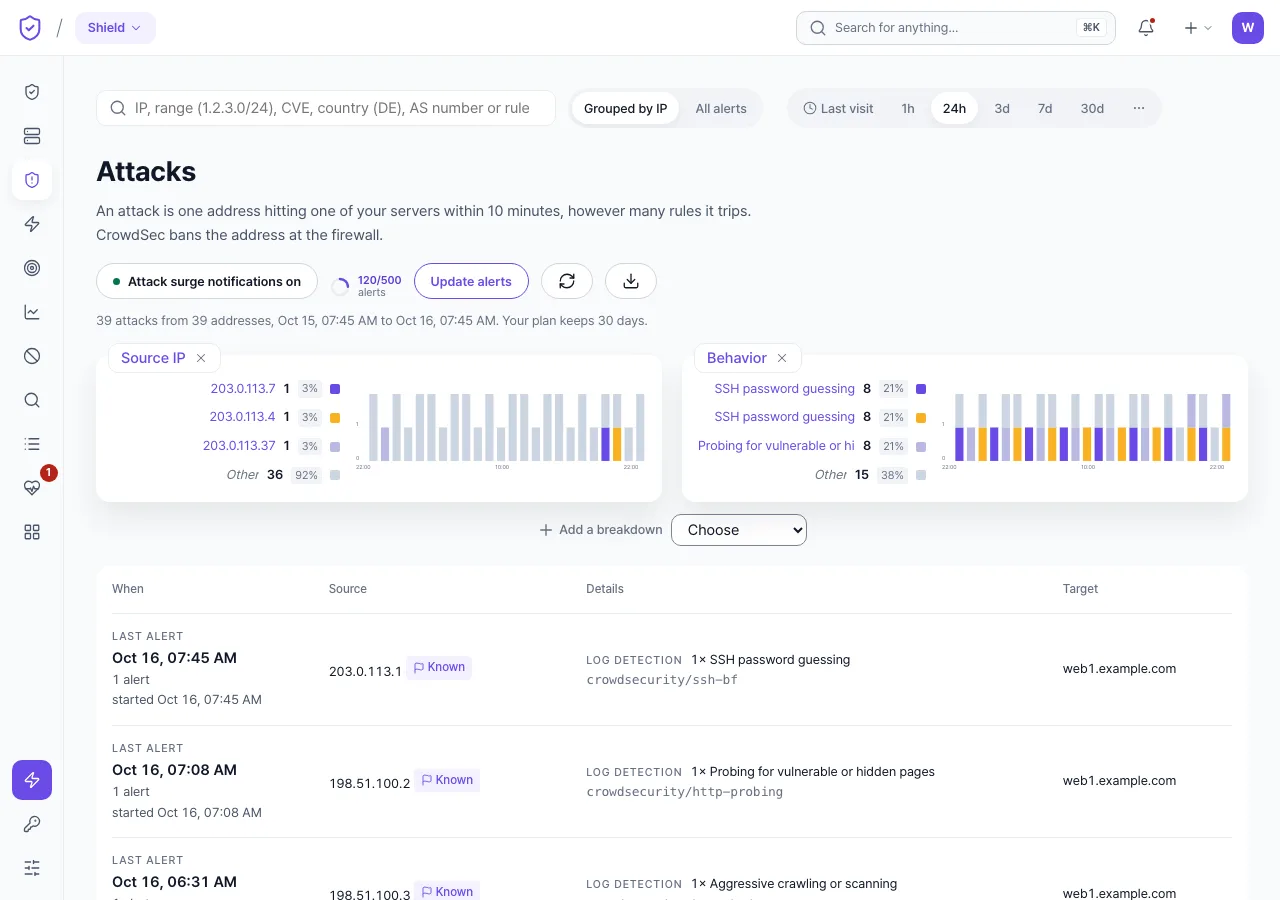
Attacks
Every blocked attack, explained. Attacks are grouped by address, with the rule that caught each one in plain words. Search by IP, range, CVE, country, AS number or rule, switch between the last hour and 30 days, break the list down by source or behaviour, and download it as a file. Screenshots on this page use sample data in a test workspace.
Unretouched screenshots of the dashboard, resized, showing a test workspace.
Not yet
- Paid plans. Licenses are not sold yet. A workspace can start a 30-day Pro trial from the dashboard without a card; when it ends, the workspace continues on Free and protection on the servers keeps running.
- Linux distributions outside the Debian and RHEL families (for example Arch, Alpine or SUSE) and Windows servers are not supported.
AZET Shield reduces common attacks. It does not guarantee that a server or site cannot be attacked or compromised. What the agent sends is listed in the privacy policy.
Plans
Open beta: start on the Free plan today at shield.azet.io, with a 30-day Pro trial inside the dashboard. To keep a paid plan, buy a license below and enter its key in the dashboard. Surface is not on sale yet.
Free
1 server or site, community blocklist, email alerts, one vulnerability scan a month, 30-day history
$0 free
Start freePro
per server or site, Gate bot check, weekly vulnerability scan, 90-day history
$9 / month
BuyStart freeSurface
external attack-surface monitoring: subdomains, exposed services, lookalike domains, certificate expiry
$99 / month
Start freeFree
1 server or site, community blocklist, email alerts, one vulnerability scan a month, 30-day history
$0 free
Start freePro
per server or site, Gate bot check, weekly vulnerability scan, 90-day history
$90 / year
BuyStart freeVulnerability scans named in the plans run on schedule against sites you have proved you own. The Surface plan adds a daily attack-surface scan (subdomains, open ports, lookalike domains, certificate expiry) for sites proved by a DNS record. Surface is not on sale yet; the other paid plans are.
Prices are in US dollars and may change; taxes may be added depending on where you live. Paid licenses bought on azet.io come with a 30-day money-back guarantee (refund policy). A lifetime license has no renewal charge and lasts for as long as AZET offers the product (details). The consumer apps are unlocked by a license key, not an account.
Questions
Which servers does it run on?
Debian and Ubuntu, and the RHEL family: RHEL, Rocky Linux, AlmaLinux, CentOS Stream, Fedora and Amazon Linux 2023. The installer stops with a message on anything else.
I lost the access token. How do I get back in?
On the sign-in page at shield.azet.io choose “Lost the token? Email me a sign-in link”. The link goes to the address you confirmed for the workspace, and your token stays as it is.
How do I remove it?
Run uninstall.sh on the server: it removes what the installer added and leaves a CrowdSec that was there before untouched. Deleting the workspace in the dashboard deletes its servers, findings, history and email address.
What does the agent send to AZET?
What it sends is listed in the privacy policy. Detection and blocking run on your server, in the open-source CrowdSec engine.
At a glance
| Status | Open beta · Free plan and 30-day Pro trial available |
|---|---|
| Operated by | AZET LLC |
| Platforms | Debian, Ubuntu and RHEL-family servers (RHEL, Rocky Linux, AlmaLinux, CentOS Stream, Fedora, Amazon Linux 2023), managed in a web dashboard |
| Access | A workspace access token, shown once when you create the workspace, or a license key. No account. |
| Free trial | 30 days of Pro, started from the dashboard, one per workspace, no card |
| Terms and refunds | Terms of service · Refund policy · Privacy policy |
| Help | hello@azet.io |
| Open-source parts | Open-source notices |
Start with one server on the Free plan.
Start freeOpen beta · Free plan and 30-day Pro trial available